 Documentation
Set capabilities and policies
Before you start
Use the institution or entity context relevant to the task. Confirm the member or administrator scope. Account sign-in, verified affiliation, entity ownership, and protocol permissions remain distinct.
Follow the task
-
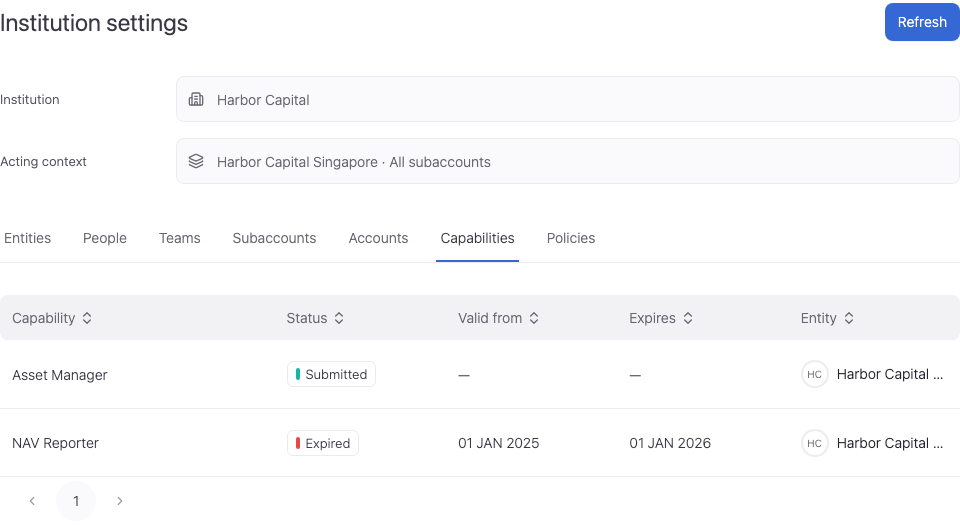
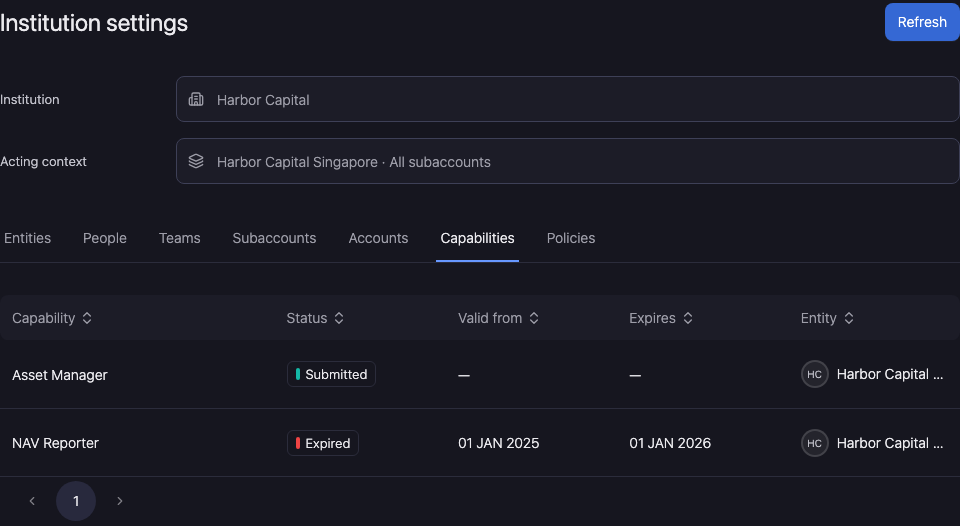
Open Capabilities for the institution and selected member, team, or entity.
-
Review the proposed capability or policy change against the current enforced scope and administrator authority.
-
Complete the supported update and verify the saved capability. Test access through the affected workspace without assuming display roles grant it.
Related settings
Use the detailed procedure for the task's field meanings, conditional paths, and operating constraints.
The Institution pages and controls lists the current application locations, registered input controls, and supported action inputs. Read-only values are distinguished from editable forms.
Check the outcome
After a change, use its operation or transaction reference to find the saved record. Reload before relying on new values.
A pending approval or signature shows progress. Check the action-specific result described in the procedure.
Resolve a blocked task
Check the active account, entity, network, authority, required saved dependencies, validation, and data freshness. If an operation is already pending, inspect it before submitting another action.
Use Troubleshooting for missing records, expired items, stale sources, rejected wallet steps, and delayed saved state.